
Smart Contract Vulnerability Assessment: How to Secure Blockchain Applications
Smart Contract Vulnerability Assessment: How to Secure Blockchain Applications
Blockchain applications are transforming financial services, digital ownership, decentralized governance, and online transactions. At the center of many of these systems are smart contracts that automatically execute predefined instructions and manage digital assets. However, vulnerabilities in contract code can expose applications to financial losses, unauthorized operations, and unexpected behavior.
A smart contract vulnerability assessment helps development teams identify potential weaknesses in their blockchain applications before attackers can exploit them. Combined with a comprehensive smart contract audit, this process can help organizations evaluate contract logic, examine security controls, and improve the resilience of decentralized applications.
What Is a Smart Contract Vulnerability Assessment?
A smart contract vulnerability assessment is a structured examination of blockchain code and its related components to identify security weaknesses. It focuses on understanding how a contract operates, how users interact with it, and whether unexpected inputs or transaction sequences could produce unintended results.
The assessment may cover access controls, token transfers, external contract calls, business logic, upgrade mechanisms, and interactions with third-party protocols.
Unlike a review focused exclusively on code quality, a security assessment considers how vulnerabilities could affect the confidentiality, integrity, and availability of the overall application, along with the protection of digital assets.
Why Smart Contract Security Matters
Smart contracts often control important operations without requiring manual approval for every transaction. Once deployed, their behavior may be difficult to change, depending on the architecture and available upgrade mechanisms.
An overlooked vulnerability could allow an attacker to bypass restrictions, manipulate calculations, exploit permissions, or disrupt important contract functions.
A professional smart contract security audit can help identify these weaknesses before deployment. Early security testing also gives developers an opportunity to address problems before the application begins handling real transactions or valuable assets.
Common Smart Contract Vulnerabilities
Understanding common vulnerability categories helps developers prepare for a more systematic security review.
Reentrancy Attacks
Reentrancy occurs when an external interaction allows a function to be called again before the original execution has safely completed. If the contract updates its state incorrectly, repeated execution may produce unintended results.
Auditors examine external calls, state changes, and interactions between functions to identify potential reentrancy risks.
Access-Control Errors
Smart contracts may contain privileged functions for changing configuration, managing permissions, minting tokens, or upgrading implementations.
If these functions are not adequately protected, unauthorized accounts may gain access to sensitive operations. Reviewing ownership, role assignments, administrative permissions, and initialization logic is therefore essential.
Business-Logic Flaws
A contract can compile successfully and pass ordinary functional tests while still implementing an incorrect business rule.
For example, a reward calculation might distribute more tokens than intended, or a withdrawal function might fail to enforce a required condition. Manual code review helps determine whether contract behavior matches the project's documented requirements.
Oracle Manipulation
Applications that rely on external price feeds or other data sources may be vulnerable when those inputs can be manipulated or become unreliable.
Security testing should examine how external data is validated, how stale information is handled, and whether the application has appropriate safeguards against abnormal values.
Unsafe External Interactions
Contracts frequently interact with other contracts, libraries, and protocols. These dependencies can introduce unexpected execution behavior or expose the application to risks originating outside its own codebase.
A comprehensive review should consider the trust assumptions and security implications of these integrations.
How to Perform a Smart Contract Security Assessment
A structured assessment typically involves several stages, adapted to the blockchain platform and application architecture.
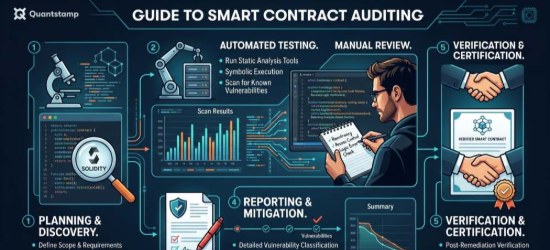
Scope definition: Identify the contracts, dependencies, functions, and integrations included in the review.
Architecture analysis: Understand how components communicate and how assets, permissions, and data move through the system.
Automated testing: Use appropriate security tools to identify known vulnerability patterns and suspicious code structures.
Manual code review: Examine business logic, access controls, transaction sequences, and potential attack paths.
Vulnerability validation: Reproduce suspected issues in a controlled environment where appropriate to understand their actual impact.
Reporting and remediation: Document findings, explain their potential consequences, recommend fixes, and retest corrected code when included in the engagement.
Combining these stages provides a more complete understanding of potential risks than relying on automated scanning alone.
Automated Tools and Manual Code Review
Automated security tools can analyze large codebases efficiently and identify common patterns associated with vulnerabilities. They are useful for repetitive checks and for highlighting code that requires additional investigation.
However, automated tools may not fully understand a protocol's intended economic behavior or complex interactions between contracts.
Manual review helps bridge this gap by examining how individual functions work together and whether the implementation follows the intended design.
For projects managing valuable assets, a thorough smart contract audit should use appropriate automated techniques alongside expert analysis and targeted testing.
The Importance of Pre-Deployment Testing
Testing before deployment allows developers to identify weaknesses while the code is still being developed and refined.
This is particularly important for decentralized finance platforms, token systems, NFT marketplaces, and governance applications where contract behavior can directly affect users and digital assets.
Before deployment, teams should review privileged functions, test critical transaction flows, examine external dependencies, and verify that security fixes have been implemented correctly.
A pre-deployment assessment cannot guarantee that every vulnerability will be discovered, but it provides a structured opportunity to identify and address known risks.
What Should a Smart Contract Audit Report Include?
An audit report should clearly communicate the assessment scope, methodology, findings, and recommended actions.
Depending on the engagement, it may contain an executive summary, contract details, vulnerability descriptions, severity classifications, affected functions, technical evidence, and remediation recommendations.
Clear reporting allows developers to prioritize issues based on their potential impact and understand how to resolve them.
Organizations should also maintain records of remediation work so that subsequent reviews can establish which findings have been addressed and which risks remain.
Integrating Smart Contract Security Into Development
Security is most effective when it is considered throughout the development lifecycle rather than only before launch.
Developers should follow secure coding practices, maintain accurate documentation, test important functions, review dependencies, and evaluate significant changes before releasing them.
Version control is also important because it helps teams identify exactly which code was assessed and which changes occurred afterward.
When a contract is upgraded or its business logic changes significantly, additional security testing may be necessary to evaluate the updated implementation.
Smart Contract Security Beyond the Blockchain
A blockchain application may include websites, APIs, cloud infrastructure, wallets, authentication systems, and administrative interfaces alongside its smart contracts.
These connected components can introduce risks that a contract-only review does not cover.
Organizations seeking a broader security assessment can complement smart contract auditing with red team services. Adversary simulation can help evaluate realistic attack paths across connected applications, infrastructure, and security controls.
Combining these approaches helps organizations examine both contract-level vulnerabilities and the wider environment in which their blockchain applications operate.
Choosing a Smart Contract Security Provider
When selecting a security provider, organizations should consider experience with the relevant blockchain platform, programming language, contract architecture, and vulnerability categories.
It is useful to understand the provider's testing methodology, manual review process, reporting standards, and approach to remediatio n validation.
The assessment scope should also be clearly documented. Knowing which contracts, dependencies, and integrations were examined helps stakeholders understand the coverage and limitations of the results.
Conclusion
Smart contract vulnerabilities can affect transaction integrity, access permissions, application functionality, and digital assets. A structured vulnerability assessment helps development teams examine these risks and identify weaknesses before they become more difficult to address.
A comprehensive smart contract security audit combines automated analysis, manual code review, targeted testing, clear reporting, and remediation verification. When integrated into an ongoing security program, these practices can help blockchain projects improve resilience as their code, dependencies, and functionality evolve.
For organizations building decentralized applications, making security a continuous development priority is an important step toward creating more reliable blockchain systems.
Comments
0